Making firewall records useful in daily operations
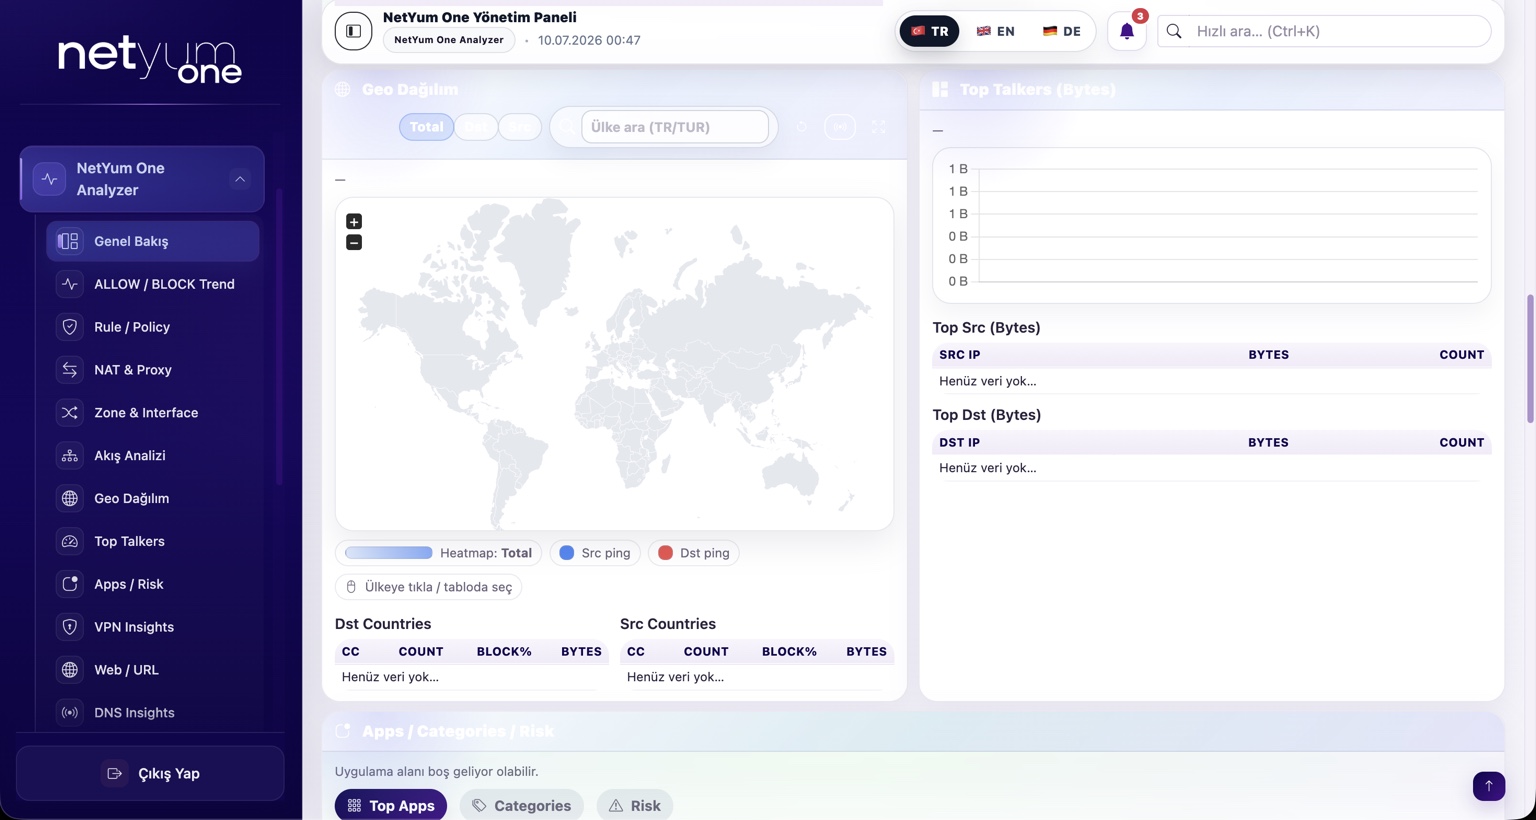
Traffic and system events from Sophos Firewall provide a starting point for troubleshooting. A Netyum One Analyzer integration project defines which event types matter and which operational questions the resulting reports should answer. A purposeful collection scope makes reports more useful than collecting everything indiscriminately.
Investigating a blocked connection requires time, source, destination and policy context to be read together. The pilot therefore checks not just delivery, but the interpretation and filtering of different event samples.
Where does Netyum One fit?
Cloud Hotspot focuses on guest access and portal management; Analyzer focuses on network-event visibility. Endpoint DLP is a separate layer for data movement on endpoints. Keeping these roles distinct makes the expected integration outcome clear: connecting a firewall does not mean every endpoint policy has also been deployed.
Pre-project checklist
- Selected log types and severity
- Time synchronization and source identity
- Blocked and permitted event samples
How is the rollout organized?
Start by identifying the deployed version, network design and responsible people. Select a limited pilot and document expected results for both successful and unsuccessful scenarios. Plan the wider rollout after acceptance checks. Repeating the same examples after an update makes changes in behavior easier to recognize.
Let’s assess your setup
Share the product version, number of locations and your main operational priority. Together, we can define the integration scope and pilot steps.